
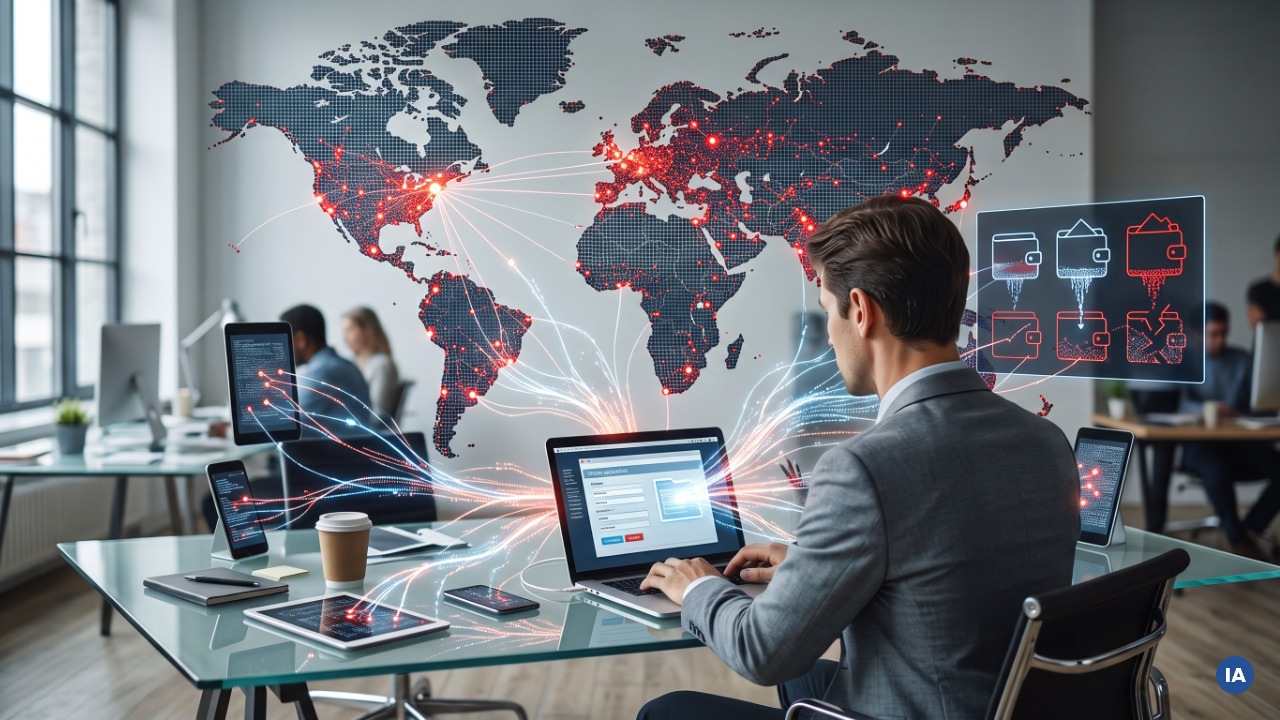
A fake job offer, a technical test, a file to download: this was enough for North Korean hackers to take control of a computer. An investigation conducted by FBIUS Department of Defense, Japanese, Australian and German authorities reconstructed a campaign that infected 30,000 devices in over 100 countriesemptying 7,000 cryptocurrency wallets for more loot than 10.7 million dollars diverted to Pyongyang.
The joint advisory, published on Friday 18 September, bears the signatures of the FBI and the Pentagon’s Cyber Crime Center, the Japanese police, the German intelligence services and the Australian Cyber Security Agency. The group, traced with the name WaterPlum (also known as Contagious Interview), has been active since 2023 and acts both to finance the regime and for industrial espionage activities. The time window of the described campaign goes from December 2025 to July 2026.
The victims, mostly software developers, web designers and cryptocurrency, blockchain and Web3 specialists, are approached on social networks, work platforms, gig economy sites and freelance marketplaces. From here the script begins: a virtual technical interview or programming test, followed by a request to download and run a file, presented as part of the assignment or as a solution to a supposed problem with the video conferencing software.
The investigators, in the official advisory, report that the malicious files are hosted on collaborative development platforms and code repositories, including Compromised NPM packages. Once executed, they steal passwords saved in the browser, screenshots, files and data from crypto wallets, also opening a hole in the victim’s corporate network, with the real risk of intellectual property theft and espionage.
False selectors, real extortionists: this is how 30 thousand devices were infected
The campaign is intertwined with a related phenomenon: North Korean citizens posing as remote IT workers, hiding their identity and real location. The images of the stolen documents also serve to impersonate victims to obtain contracts and collect payments in foreign currency. In at least one case a fake collaborator has extorted a company threatening the publication of the proprietary source code, which was then actually released online; in another he deliberately damaged the website he had been hired to maintain.
During the interviews, WaterPlum operators use software from face-swapping based on artificial intelligenceonly to then deactivate the camera citing network problems. They prefer to be paid in cryptocurrency, often on accounts held by third parties so as not to leave direct traces. The detail reported by the investigators is curious: on North Korean national holidays, the attackers suspend their activity to play online or watch football matches.
Authorities link WaterPlum to the 313th General Officea department of the North Korean Department of Munitions Industry which also deals with military research. A detail that undermines the narrative of the “remote collaborator in search of fortune”: behind an apparently harmless job interview an intelligence operation financed by an entire state apparatus may be hidden, not a single opportunistic cybercriminal.
